Critical PHP Flaws CVE-2026-109618: What to Do Now
PHP patched two critical flaws (CVSS 9.2) that allow takeover without a login. What to do today, and how to leave the patch treadmill for good.
On 21 October 2026 the PHP project shipped emergency releases for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619. Both are rated 9.2 out of 10 on CVSS 4.0. Both can let an attacker run code on a web server without logging in. If your website runs on WordPress, WooCommerce, Joomla or any other PHP stack, this one is worth ten minutes of your day.
This post covers what happened, what to do right now, and why the same story keeps repeating for older sites.
What happened
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two flaws in how PHP handles memory between web requests:
- CVE-2026-109618, “RCE via OOM corruption”. When PHP runs out of memory at the wrong moment, it can leave half-initialized request data behind, and request cleanup may then treat that data as valid.
- CVE-2026-109619, “RCE via stale global state”. Internal state from one request can survive after its memory was freed, and a later request handled by the same worker can use it.
The PHP security team says the risk is highest on Apache with mod_php. There, they demonstrated an exploit where an unauthenticated request triggers the attack before any of the site’s own code runs. PHP-FPM, php-cgi, FrankenPHP and LiteSpeed setups are also listed as at risk.
Their advice leaves no room for interpretation: configuration tweaks reduce exposure, but updating is the only complete fix.
Who is affected
Any PHP installation serving web traffic on a version older than the fixed releases. That covers most of the small-business web: WordPress sites, WooCommerce shops, and the long tail of agency-built PHP sites nobody has touched in years.
Two details make it worse for older sites:
- PHP 8.1 and older no longer get official releases. The PHP team made an exception this time and published minimal source backports for 7.4, 8.0 and 8.1. They are meant for people who compile PHP themselves. A typical small-business site on shared hosting gets nothing from that.
- PHP 8.2 reaches end of life on 31 December 2026. A site patched to 8.2.35 today has ten weeks before it needs to move again.
Our sister agency checked the client sites it manages the day after the release. Most of them were still running an unpatched PHP version. These are sites with an agency behind them. The picture for unmanaged sites is unlikely to be better.
What to do right now
If you run a PHP site, do this today:
- Check your PHP version. In WordPress: Tools → Site Health → Info → Server. Your host’s control panel shows it too. You want 8.5.12, 8.4.27, 8.3.36, 8.2.35 or newer.
- Take a full backup first, files and database, stored off the server.
- Update PHP, or ask your host when they will. On shared hosting the host usually installs the patch, and your job is to confirm it is done.
- Update WordPress core, your theme and every plugin. Old plugins are the usual reason a PHP upgrade breaks a site.
- Test the pages that make you money: the contact form, the cart and checkout.
- Look for signs someone is already in: admin users you don’t recognize, new files, odd redirects.
If you truly cannot update yet, the php.net advisory lists interim server settings, such as disabling session.upload_progress and lowering post_max_size. They are a job for whoever runs your server, and they do not make it safe.
Why legacy sites keep getting hit
This is not PHP’s fault in particular. Every big platform ships security fixes. The problem is the shape of a typical older website:
- A long stack you have to keep current. The PHP runtime, the CMS core, a theme, and often 20 to 40 plugins. Each has its own release cycle. One stale piece is enough.
- Nobody owns updates. The agency that built the site moved on. The owner doesn’t know which PHP version they run, which is completely reasonable for someone running a bakery.
- Updates break things, so they get postponed. A plugin abandoned in 2021 stops working on PHP 8.3, and the safest-looking move is to leave everything alone.
- Old runtimes linger. Sites keep running for years after their PHP version stops receiving fixes, because nothing visibly breaks until something does.
The result is a patch treadmill. You can stay on it by paying someone to keep every layer current, and for complex shops and custom applications that is the right call. But many sites are a handful of pages, a contact form and some photos. For them, the treadmill is pure overhead.
Step off the treadmill: rebuild instead of patching
That is the case SOSEI is built for. Give it your current URL. It audits the site against 106 checks, then rebuilds it as a modern, hosted site with your content, images, logo and colors carried over. Typically that takes one to three minutes. The mechanics are in How SOSEI Rebuilds a Website in Under Three Minutes.
What changes for security:
- No PHP or WordPress for you to patch. The rebuilt site has no plugin stack, no CMS admin on your domain, and no runtime version to keep track of.
- Hosting, HTTPS, backups and updates are handled for you. There is nothing to install or maintain.
- It is watched after launch. The site is re-audited every two weeks, a Monday report flags anything new, and you can rebuild against today’s standards up to 5 times a month on the same subscription.
- You stay in control. Everything lands as a draft. Your old site stays live until you point your domain at the new one, and the domain stays in your name.
A real example: klv.ee
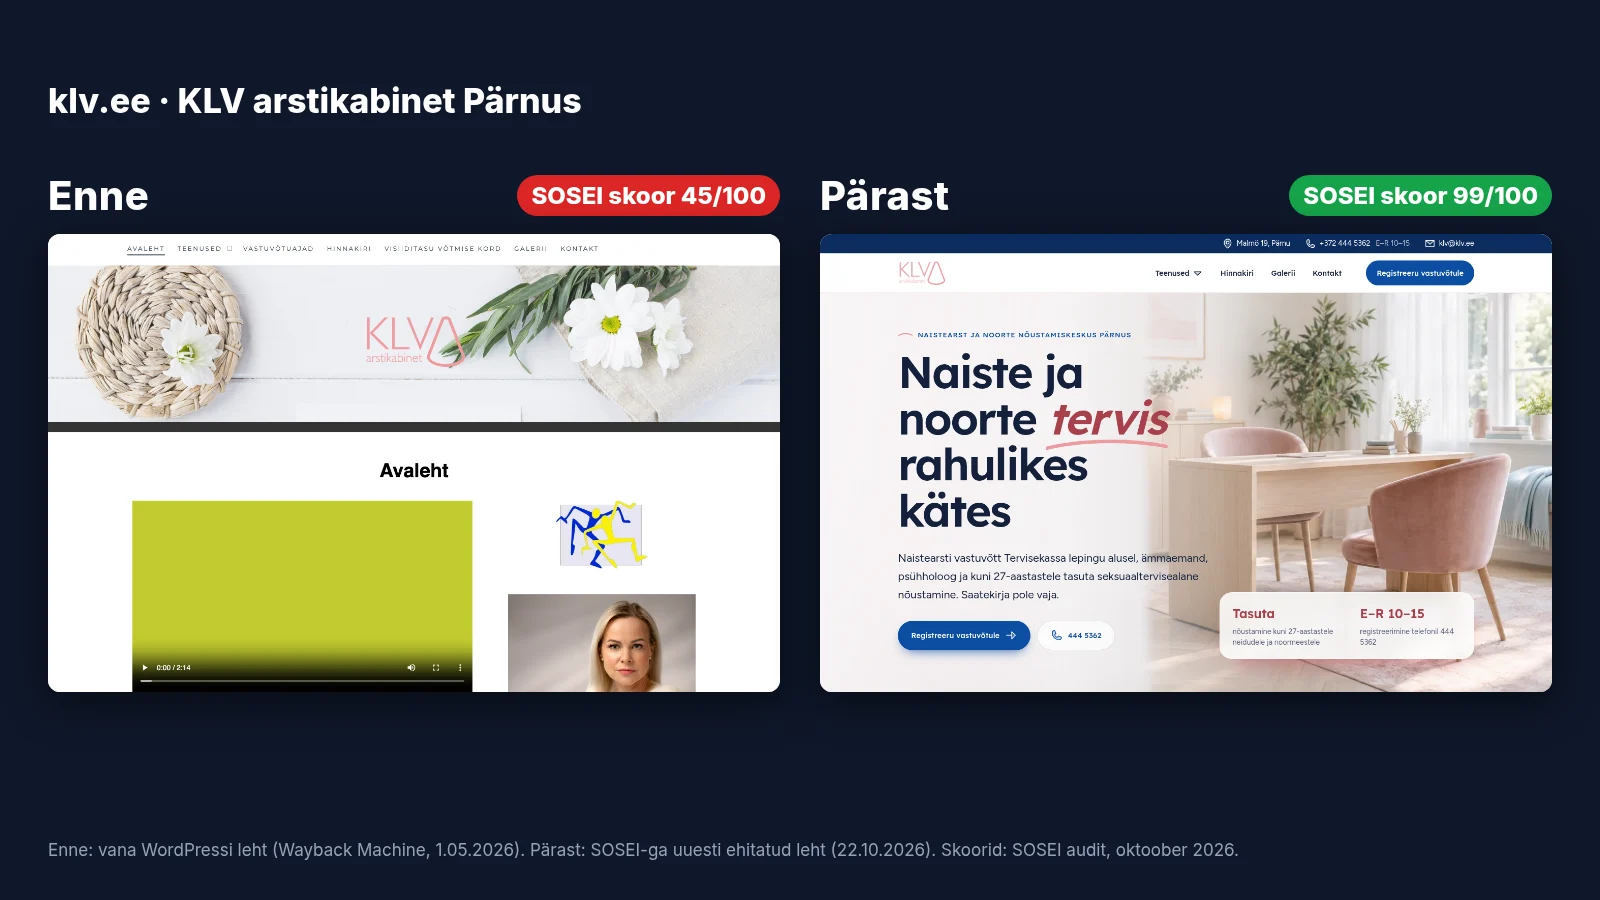
KLV, a doctor’s practice in Pärnu, Estonia, ran its site on an old WordPress install. We rebuilt it with SOSEI. The SOSEI audit scored the old site 45/100. After the rebuild, the live site scores 99/100.
| SOSEI audit | Before (old WordPress site) | After (SOSEI rebuild) |
|---|---|---|
| Overall | 45 | 99 |
| Speed | 61 | 100 |
| Privacy | 55 | 100 |
| SEO | 71 | 94 |
On mobile, the rebuilt home page’s largest content now loads in 1.3 seconds (LCP). There is no WordPress or PHP left on the site for anyone to patch.
A few honest caveats. SOSEI is a fit for business websites of up to 20 pages, with extra pages priced from your credit. It is not a replacement for a full WooCommerce shop today. If you sell online through PHP, patch first, then talk to whoever runs your store.
Pricing: €19.90 per month per website, with hosting, SSL and your own domain included. Every plan starts with a 14-day free trial, no card needed, and you can cancel anytime.
Check your site in a minute
Not sure what your site runs on, or what an attacker would see? Start with the free audit. You don’t need to sign up, and it only reads your public website.
Run the free audit or start your 14-day free trial.
Sources: php.net security advisory, 21 Oct 2026 · GHSA-w8hw-w9fx-j79w (CVE-2026-109618) · GHSA-6wmf-4rv5-p3rp (CVE-2026-109619)